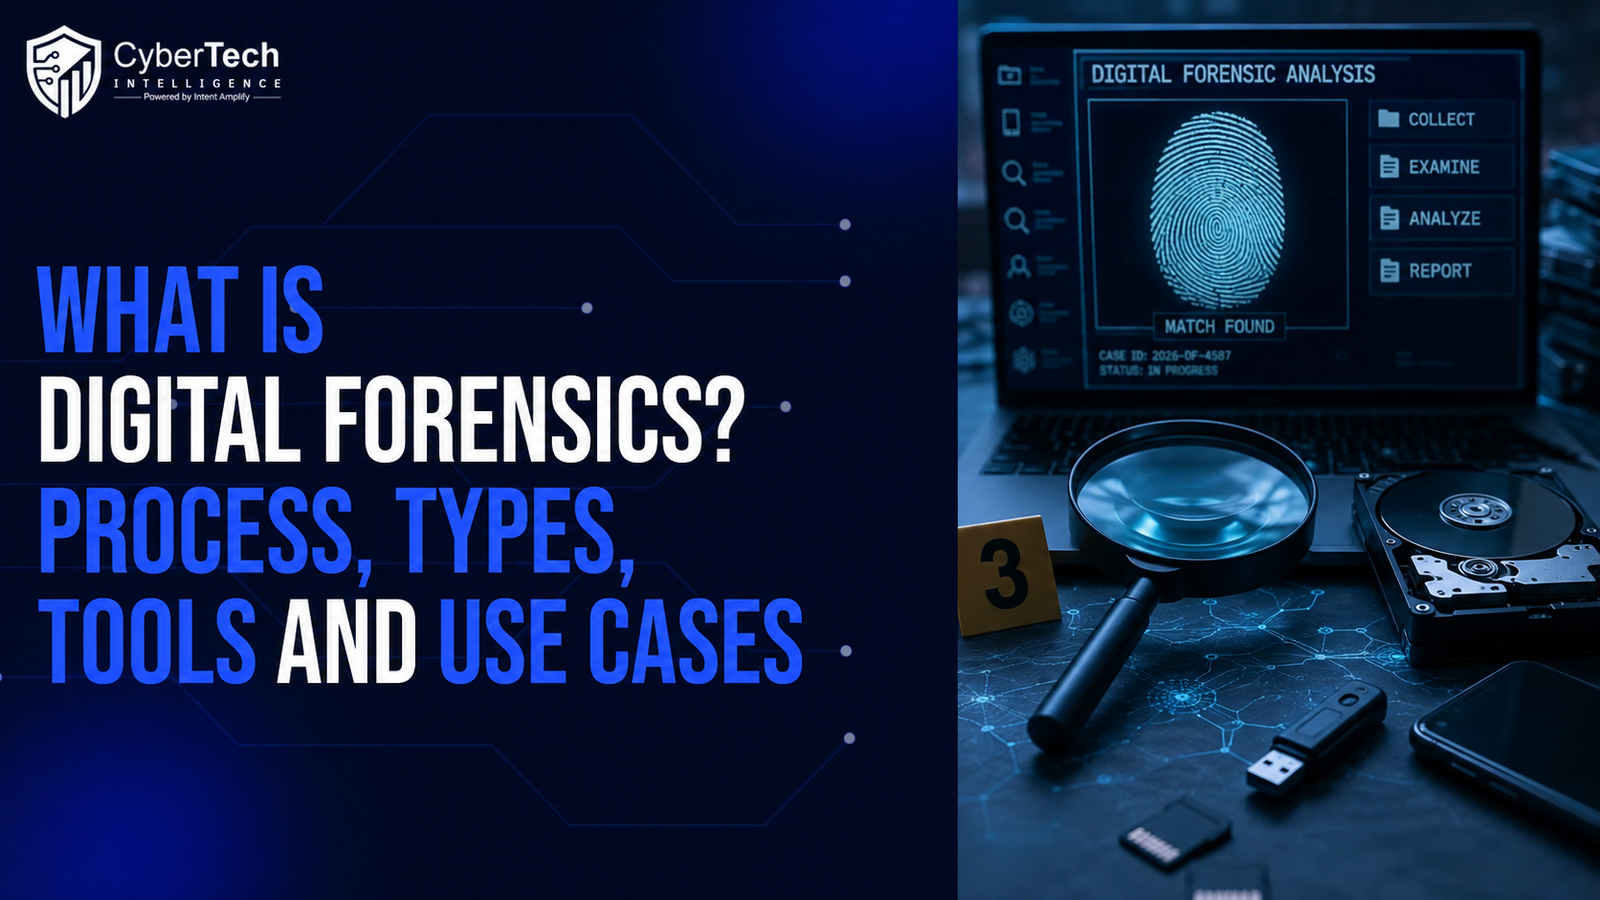
Digital forensics is the application of scientific and investigative methods to identify, collect, preserve, examine, analyze, and report information stored or transmitted electronically. A digital forensic investigation aims to determine what happened, when it happened, how it happened, which systems or identities were involved, and what evidence supports those conclusions. NIST defines digital forensics as applying science to the identification, collection, examination, and analysis of data while preserving the integrity of the information and maintaining a strict chain of custody. The discipline requires reliable and repeatable methods because findings may influence in…
Continue Reading
Complete the short form to unlock the full blog. No password required.
Author
CyberTech Intelligence Research Desk
Author